For many boards, artificial intelligence risk has largely been viewed as a question of policy, ethics, and responsible adoption. That conversation now needs to expand. The emergence of autonomous AI agents introduces a more immediate operational concern: what happens when...
Many healthcare organisations operate under an assumption that strong passwords, multi-factor authentication, and documented access policies represent effective access governance. However, authentication is only the first step. For healthcare organisations across Australia and New Zealand, the governance challenge extends beyond...
When a cyber incident occurs, technical teams carry much of the immediate operational workload. But oversight of material cyber risk cannot simply be delegated. Boards and executive leaders need to know whether the organisation can identify an incident, escalate it...
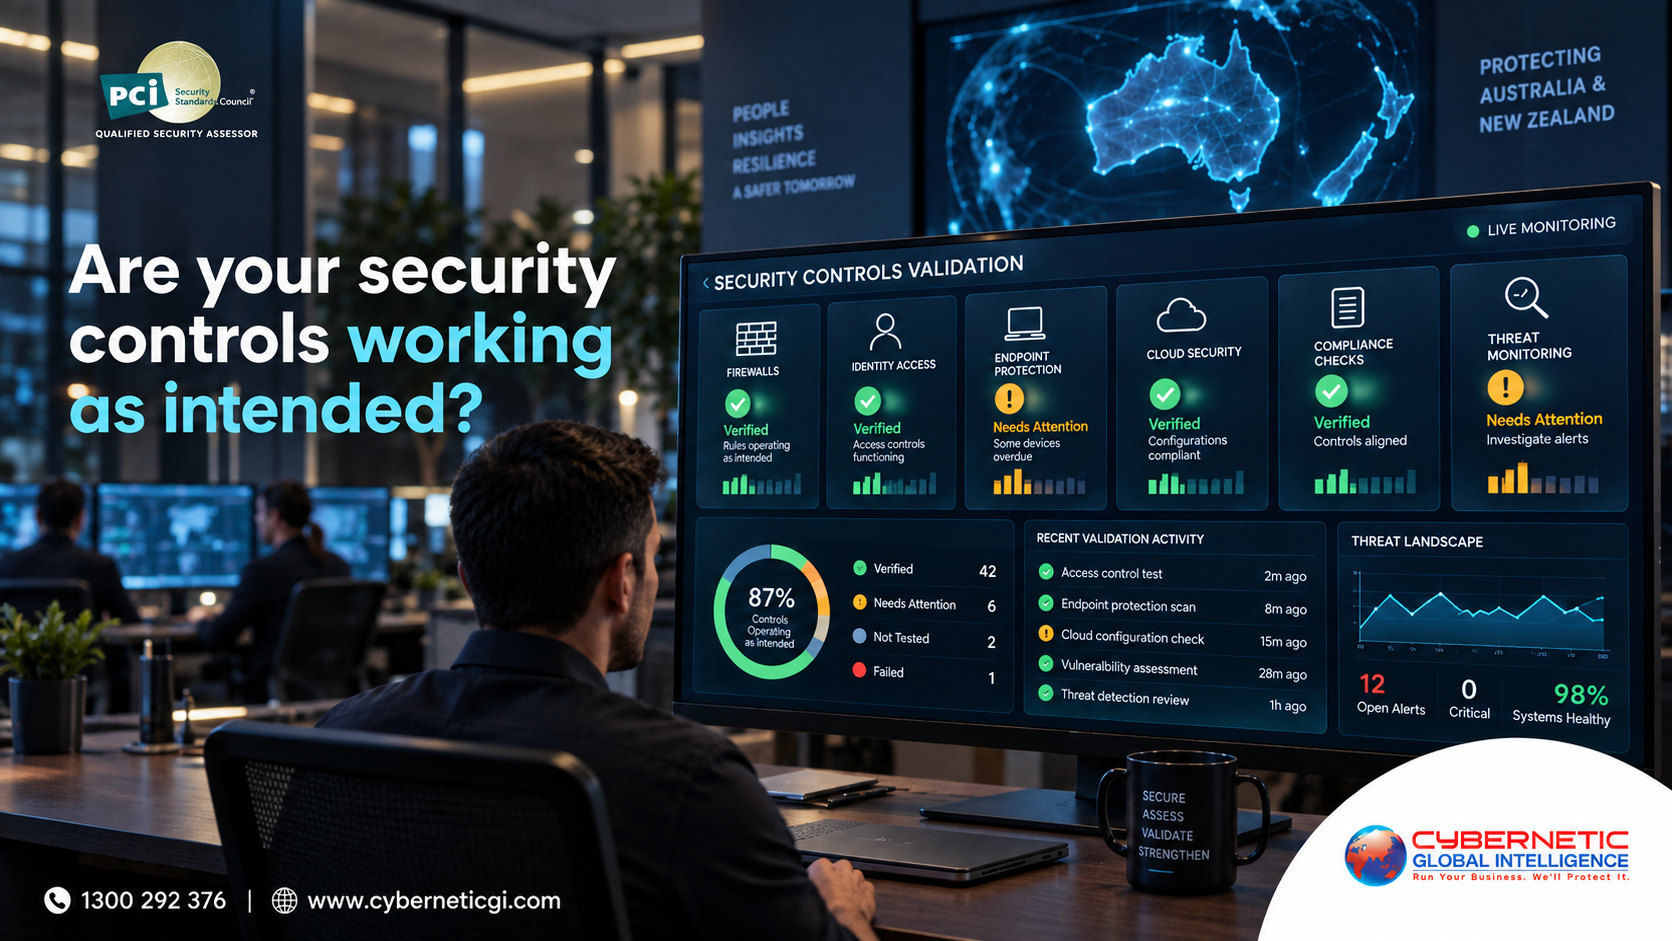
Executive confidence is often built on policies, frameworks, and reporting dashboards. A board approves an information security strategy. Leadership reviews risk indicators. Security committees receive regular updates. However, documented controls do not always reflect operational reality. Security policies must operate...
A critical vulnerability does not become a governance issue only when an attacker exploits it. The governance issue begins earlier: when an organisation cannot prove that security advisories are identified, assigned, escalated and remediated within defined timeframes. That is the...