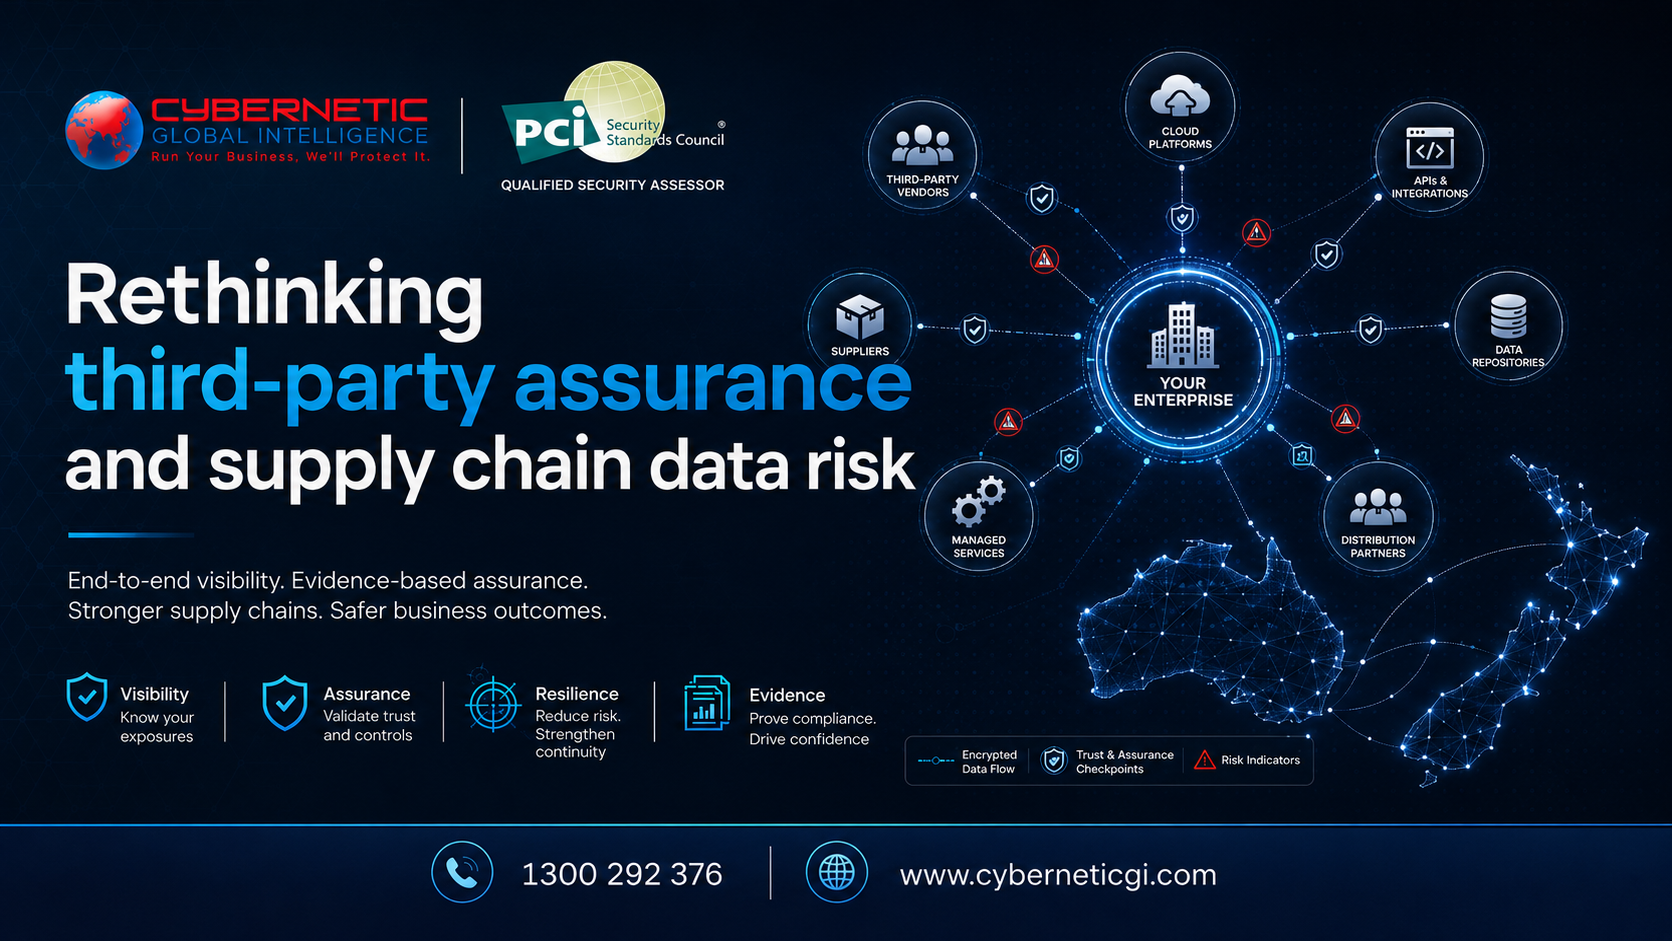
The moment customer data moves beyond your immediate operational environment, governance becomes more complex. Australian and New Zealand organisations routinely rely on external providers for customer service, technology operations, cloud platforms, and specialised business processes. Those arrangements may improve efficiency,...
Accounting firms hold some of their clients' most sensitive financial, tax and personal information. Yet access to that information rarely sits with employees alone. Contractors, external specialists and client users may all require access across different systems, often for different...
For critical infrastructure organisations, maintaining an asset register is necessary. However, the register alone does not show whether critical systems are accurately classified, monitored, securely configured and covered by effective access controls. That limitation becomes more serious as environments change....
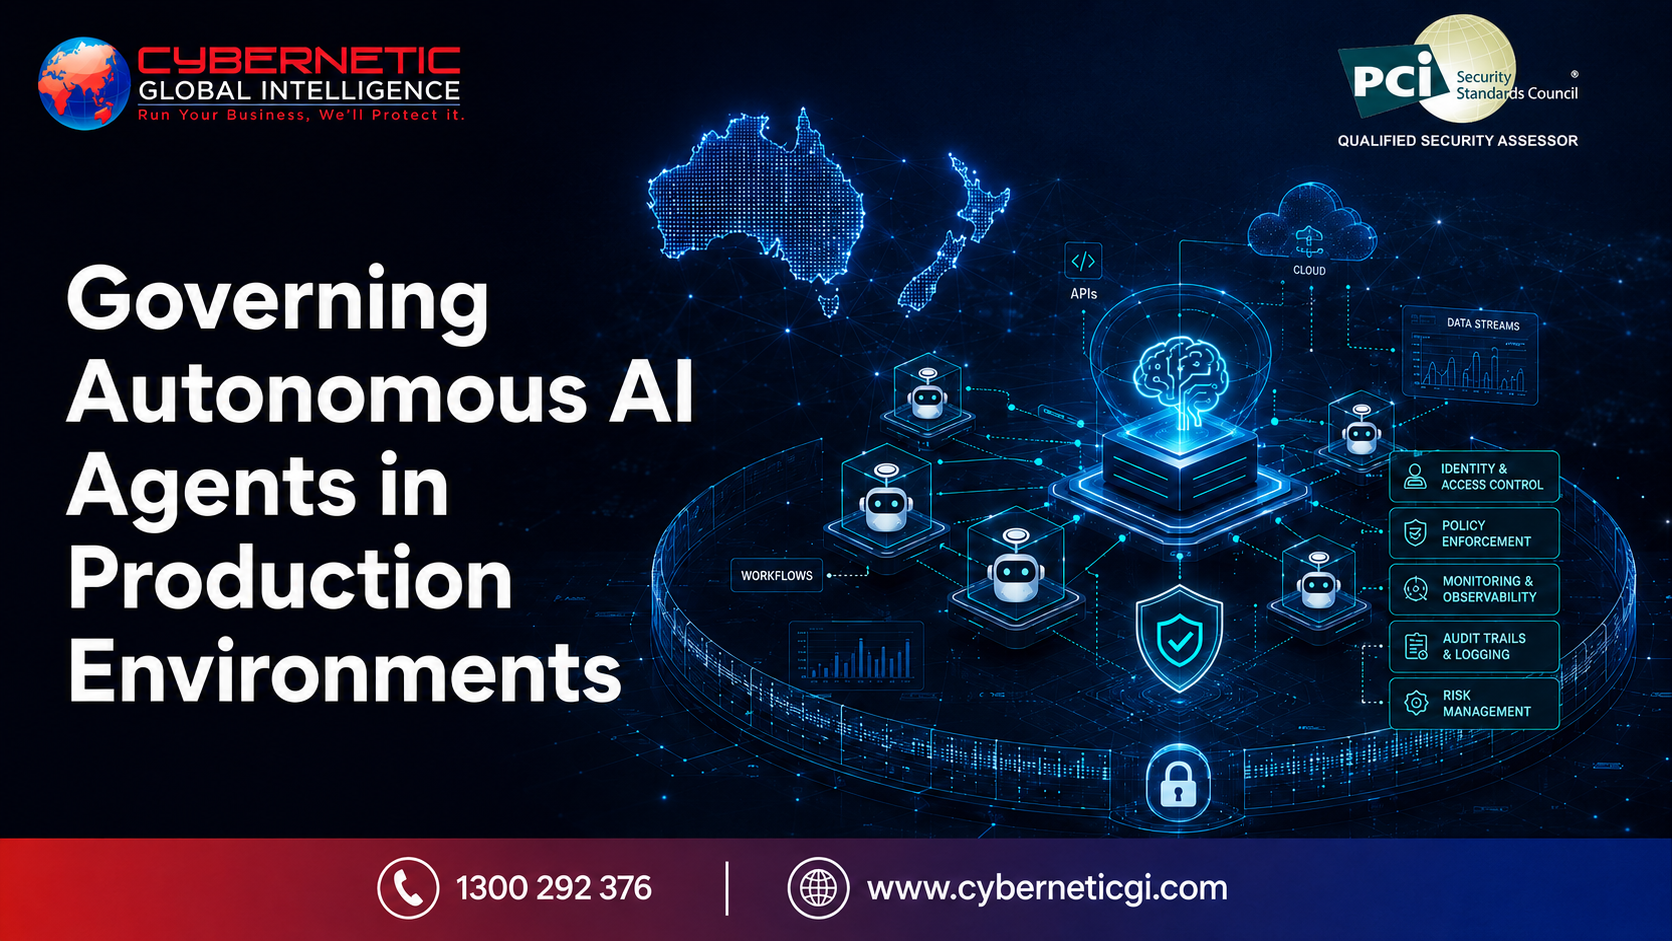
As artificial intelligence moves from generating content to taking action, the governance challenge changes with it. Agentic AI systems can reason across multiple steps, interact with external tools and APIs, and execute actions with reduced human involvement. Organisations are therefore...
When an original equipment manufacturer, or OEM, remotely connects to a factory environment, it may diagnose equipment or configure a programmable logic controller. This connection creates a temporary pathway through the organisation’s security boundary. This access may be necessary to...