Executive confidence is often built on policies, frameworks, and reporting dashboards. A board approves an information security strategy. Leadership reviews risk indicators. Security committees receive regular updates. However, documented controls do not always reflect operational reality. Security policies must operate...
A critical vulnerability does not become a governance issue only when an attacker exploits it. The governance issue begins earlier: when an organisation cannot prove that security advisories are identified, assigned, escalated and remediated within defined timeframes. That is the...
Across Australia and New Zealand, cyber resilience is increasingly a governance issue, not simply a technology issue. For bank boards, knowing that controls exist is no longer enough. The more important question is whether directors can demonstrate that critical operations,...
Temporary Wi-Fi, connected CCTV, cloud project platforms and digital access systems are changing the risk profile of construction projects. The security perimeter no longer stops at the head office. It now extends to the active construction site, where security increasingly...
Ask a CISO for an inventory of corporate laptops and the answer may be available within minutes. Ask the same organisation to account for every industrial controller, undocumented switch, legacy gateway and temporary wireless device operating across a factory floor,...
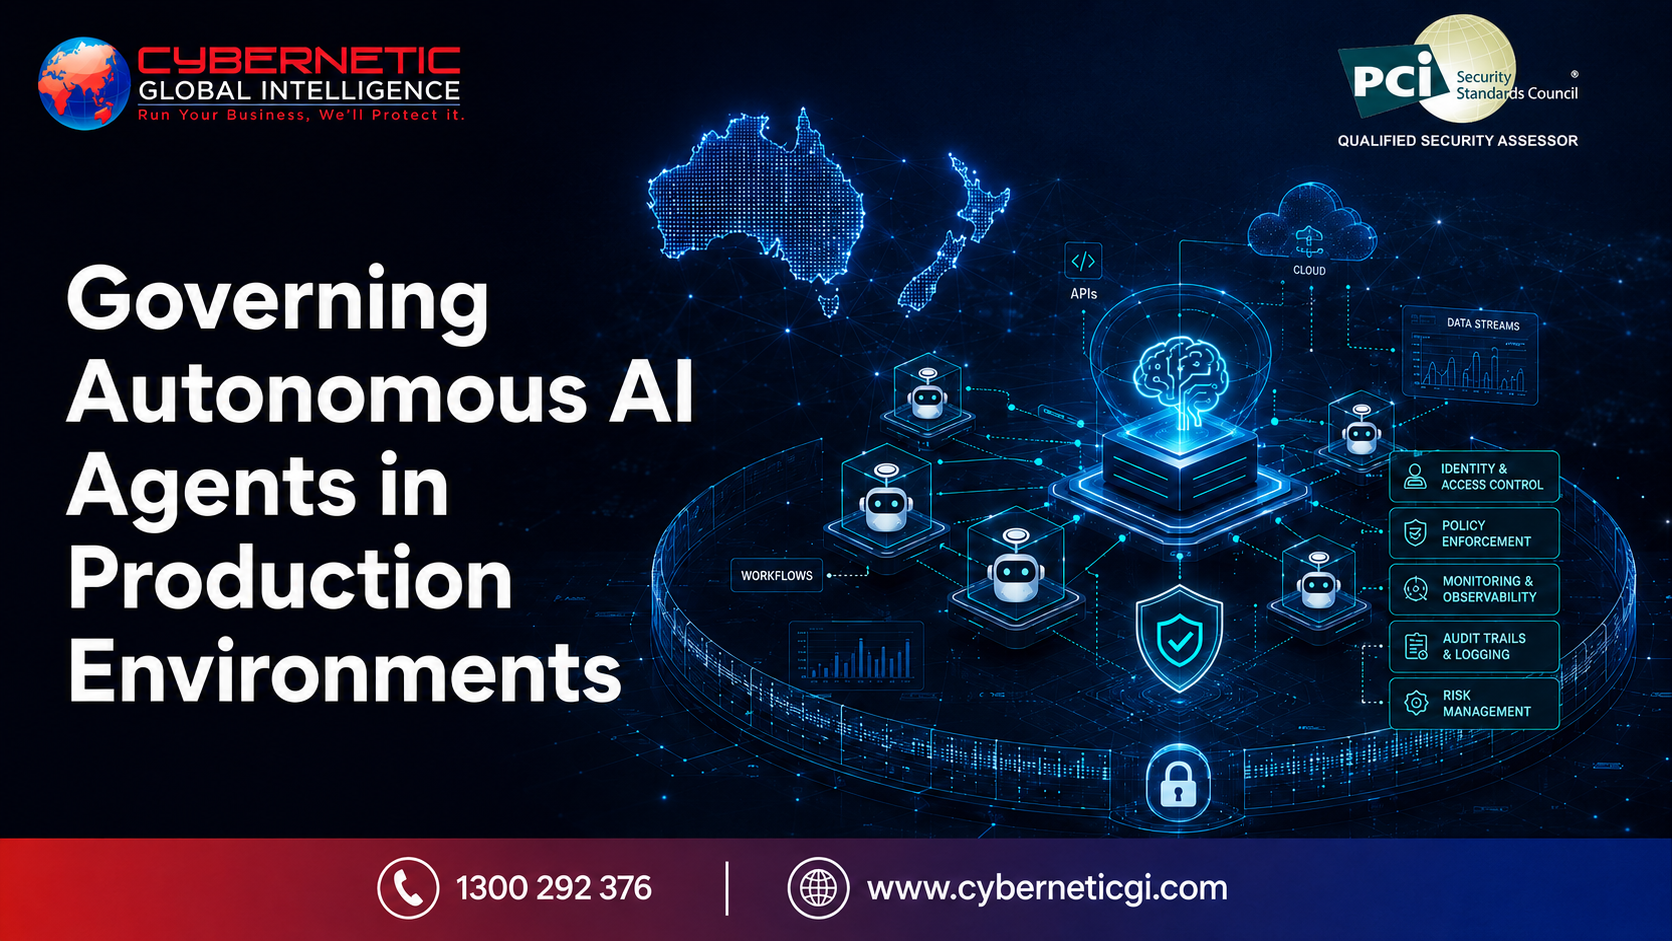
As artificial intelligence moves from generating content to taking action, the governance challenge changes with it. Agentic AI systems can reason across multiple steps, interact with external tools and APIs, and execute actions with reduced human involvement. Organisations are therefore...
In less than three weeks, three big names—Ingram Micro, United Natural Foods Inc. (UNFI), and McDonald’s—faced major data breaches. These businesses span tech distribution, food logistics, and retail. None involved complex nation-state hacks or zero-day exploits. Instead, each fell victim...