AI has been revolutionizing the sphere of cybersecurity for businesses, allowing for automation, detection of weaknesses and improvements of the cybersecurity posture. However, as AI agents become more independent and able to communicate with applications and perform commands, they also...
Many companies are blindly following the bandwagon of including AI extensively in their operations to cut costs without adequately focusing on the safeguards to manage it effectively. However, adopting AI without strict control is a recipe for disaster that can...
Many Board members may have seen the reports published by the Office of the Australian Information Commissioner (OAIC). It talks in broad terms about the huge spike in mega breaches of data in the health sector. The OAIC report shows...
Recently, the Australian Signals Directorate sounded an alarm on a severe remote code execution vulnerability that impacts PHP worldwide, dubbed PHP2Shell. It allows attackers a high chance of hijacking web applications. This, in turn, can give them full control of...
For many boards, artificial intelligence risk has largely been viewed as a question of policy, ethics, and responsible adoption. That conversation now needs to expand. The emergence of autonomous AI agents introduces a more immediate operational concern: what happens when...
Many healthcare organisations operate under an assumption that strong passwords, multi-factor authentication, and documented access policies represent effective access governance. However, authentication is only the first step. For healthcare organisations across Australia and New Zealand, the governance challenge extends beyond...
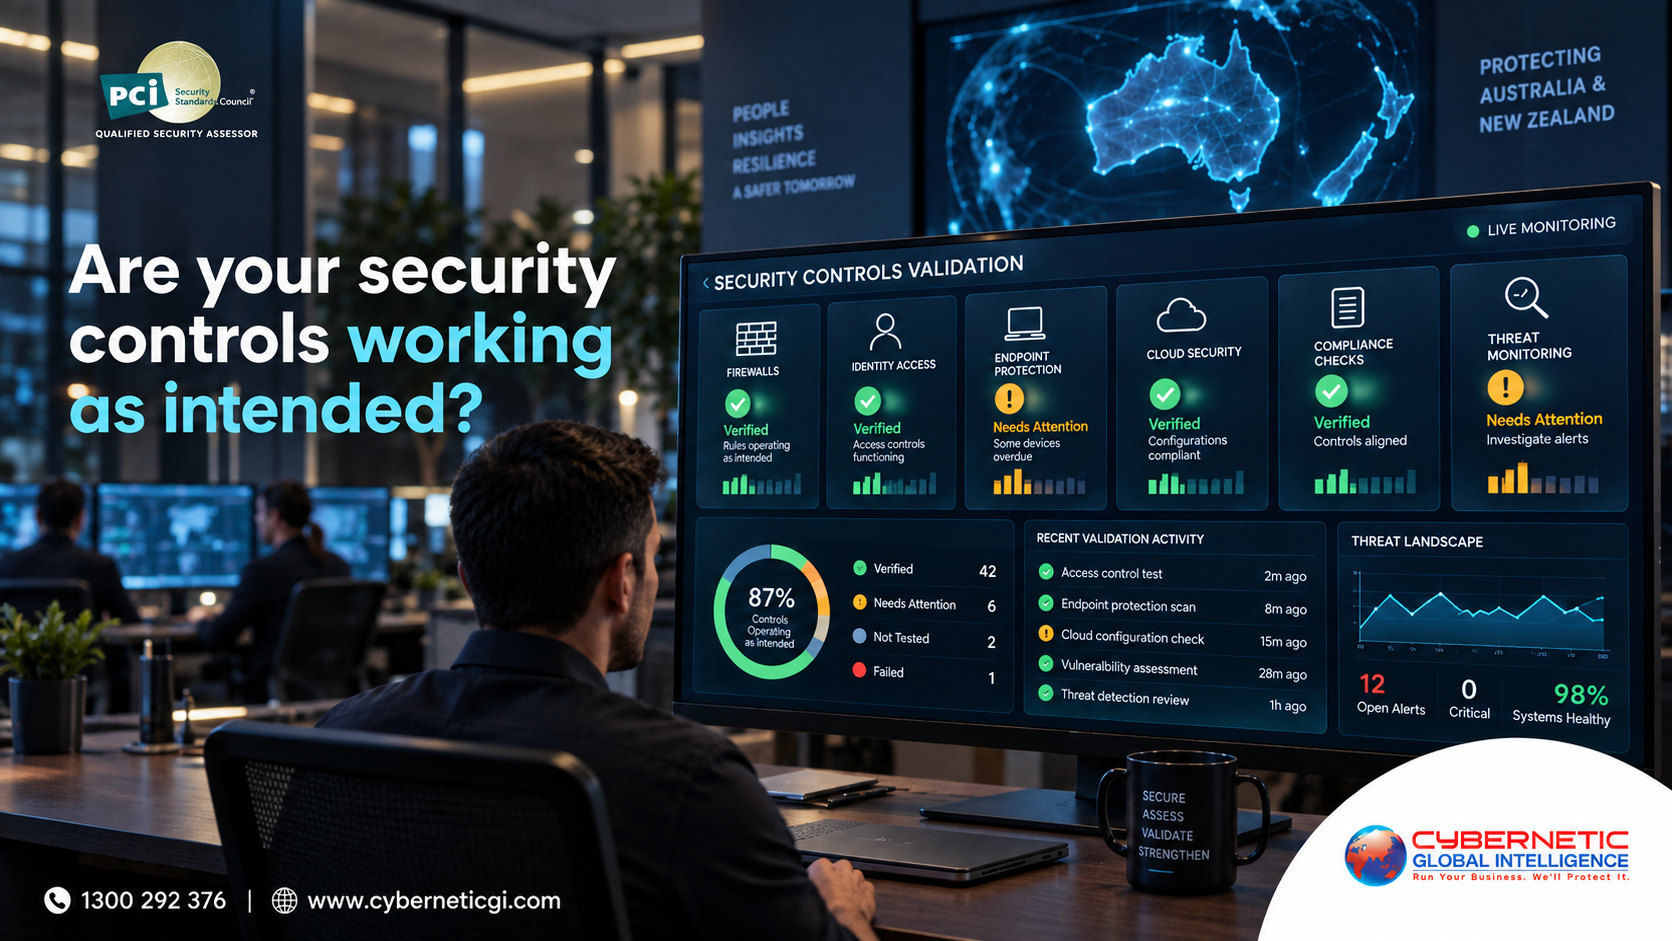
Executive confidence is often built on policies, frameworks, and reporting dashboards. A board approves an information security strategy. Leadership reviews risk indicators. Security committees receive regular updates. However, documented controls do not always reflect operational reality. Security policies must operate...