Many healthcare organisations operate under an assumption that strong passwords, multi-factor authentication, and documented access policies represent effective access governance. However, authentication is only the first step. For healthcare organisations across Australia and New Zealand, the governance challenge extends beyond...
When a cyber incident occurs, technical teams carry much of the immediate operational workload. But oversight of material cyber risk cannot simply be delegated. Boards and executive leaders need to know whether the organisation can identify an incident, escalate it...
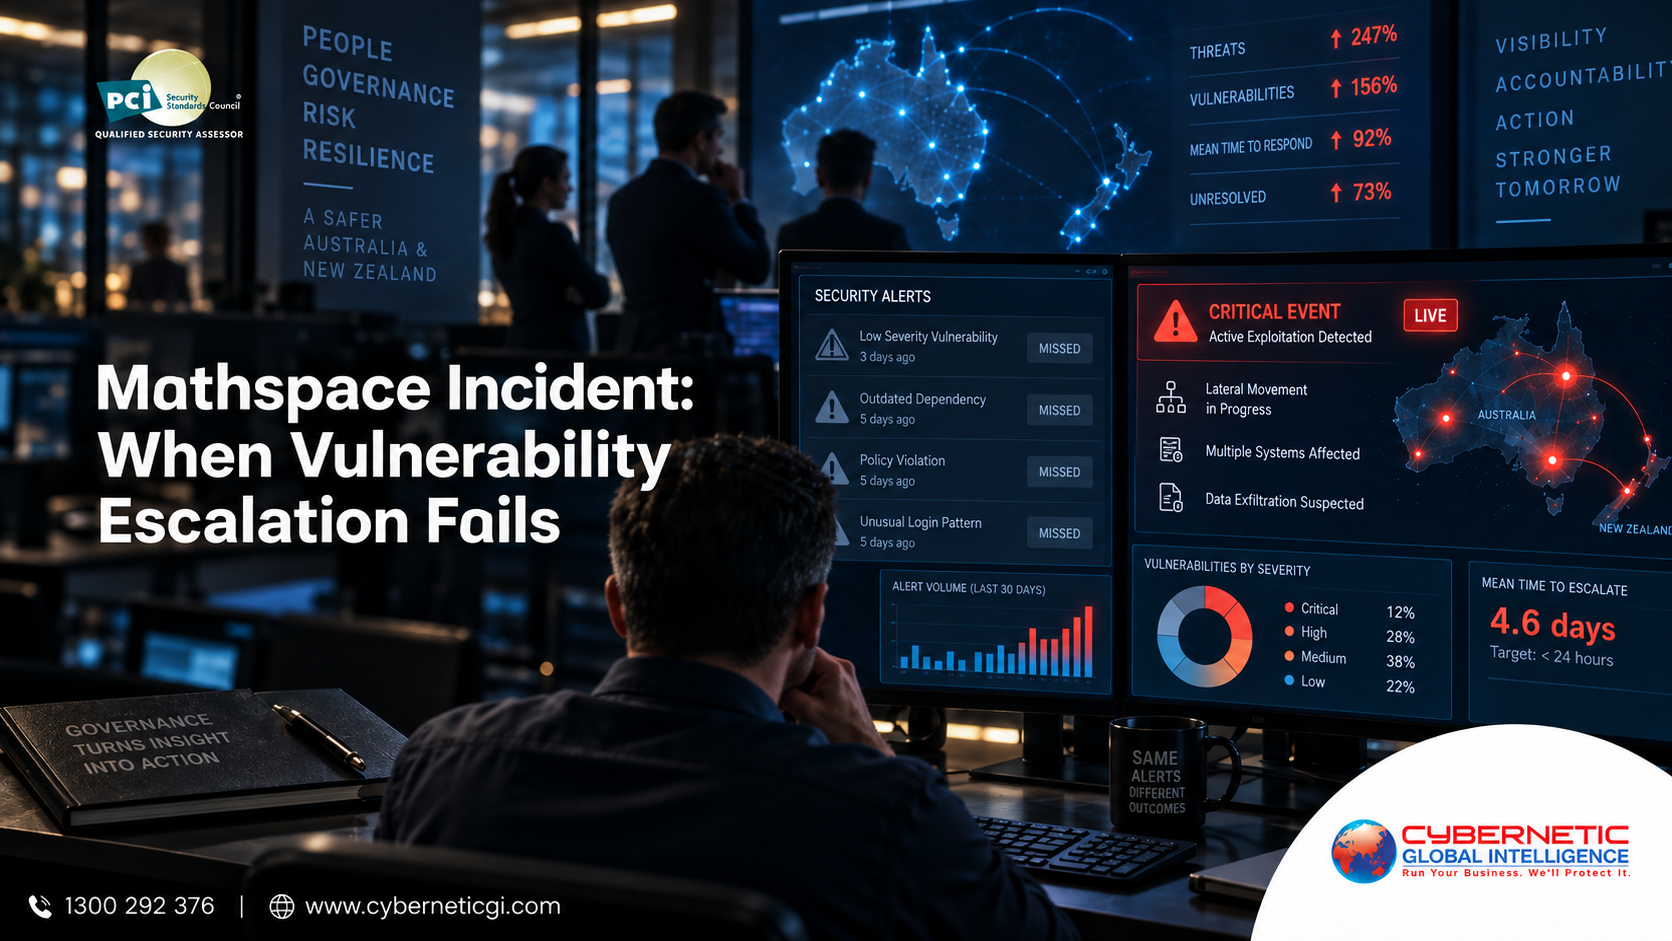
A critical vulnerability does not become a governance issue only when an attacker exploits it. The governance issue begins earlier: when an organisation cannot prove that security advisories are identified, assigned, escalated and remediated within defined timeframes. That is the...
Third parties help organisations move faster. They support IT, finance, software delivery, procurement, customer service, and day-to-day operations. But every outside vendor, consultant, contractor, or service provider also adds risk. This risk grows when third parties can access systems, data,...
A major cyber incident at a medical technology company, Stryker has become more than a headline. It is now a practical lesson in how fast a cyberattack can spill across business operations, staff access, supply chains, and customer confidence. On...
CEO CYBER SECURITY ALERT BULLETIN Global Conflict Escalation – Immediate Cybersecurity Review Required for Organisations in Australia, New Zealand, the Pacific and Global Markets Issued for: CEOs, Board Directors, CIOs, CISOs and Business Leaders Region: Australia | New Zealand |...
The modern Olympic Games run on a vast and complex digital backbone. Behind every race result, ticket scan, and live broadcast sits a network of timing systems, media platforms, athlete databases, and stadium technologies. Millions of fans, broadcasters, officials, and...

Global tensions continue to shift. Political disagreements, economic pressure, and military conflicts create uncertainty across regions. These developments often extend beyond diplomacy and trade, influencing cyber activity. Hacktivist groups and politically motivated attackers often respond to these tensions. They may...